


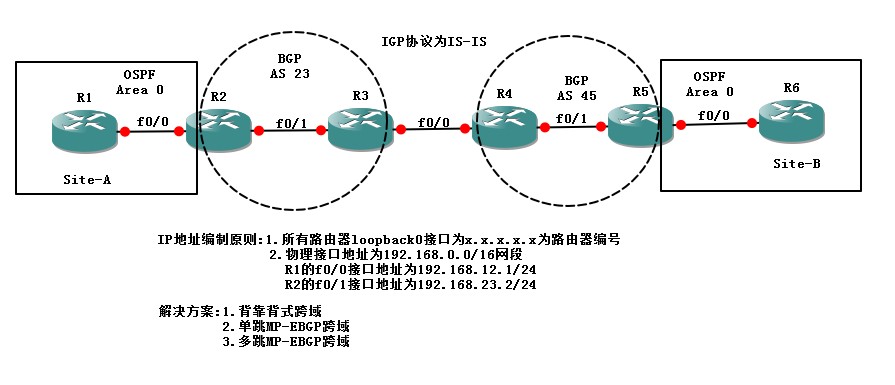
1.背景介绍.
在ISP部署MPLS VPN的时候,通常情况下仅有一个单独的BGP域,也就是我们通常的MPLS VPN配置方法.
在此去介绍一种更为使用的MPLS VPN.就是接下来介绍的跨越多个BGP域的MPLS VPN.同时也是CCIE ISP的考点.
由于配置文件比较多,所以在此将三种解决方案分开去写.
2.工作原理
这种跨域也叫单跳MP-EBGP跨域,AS内通过正常的MPLS/BGP传递VPN信息和构建LSP隧道,AS之间通过单跳的MP-EBGP协议传递VPN信息并构建LSP隧道。
如上图所示,R1通过IGP传递私网信息给R2,R2通过MP-IBGP传递VPN信息到R3,R3通过单跳的MP-EBGP传递VPN路由信息给R4,然后,R4再通过MP-IBGP传递VPN信息给R5,R5再通过IGP协议把私网信息传递给R1,至此,R6拥有到达R1的路由信息。如果中间跨域多个AS,AS内部全部按照MP-IBGP协议传递,BGP边界之间全部按照单跳的MP-EBGP传递。
当使用BGP传递路由时,如果是EBGP传递,下一跳必定改变为自己,如果通过IBGP传递,下一跳可以改变为自己也可以不改变,另外,当采用MP-BGP传递VPN路由信息,下一跳更改时,那么就需要为VPN重新分配标签。
如上图所示,在这种跨域中,R3向R4传递VPN路由时,下一跳必定改变为自己,同时R4重新为VPN分配标签,R4向R5传递VPN路由信息时,分两种情况考虑,一是R3向R2传递VPN路由信息时,下一跳改变为自己,一是R3向R2传递私网路由信息时,下一跳不改变,也就是下一跳仍然为R4。
在改变路由下一跳为R3的情况下,R3重新为VPN分配标签,VPN从R2到达R5的路径为R2→R3→R4→R5,在左边AS内,构建R2到R3的双层LSP隧道,内层为VPN标签(R3分配的),外层为R2到R3的公网隧道,在BGP边界之间构建单层LSP隧道,只携带VPN标签(R4分配的),在右边AS内构建双层LSP隧道,内层为VPN标签,R5分配的,外层为R4到R5的公网隧道。在两个BGP边界处由于VPN标签都重新分配,所以最底层的标签在两个BGP边界处都会有SWAP操作,也正是通过VPN标签的SWAP,把两个AS的VPN隧道连接起来。
如果不改变VPN路由的下一跳,那么R5接收的VPN路由的下一跳就是右边AS域内的R4,则VPN从R2到R5的路径R2→R4→R5,那么就需要构建一条从R2一直到R4的双层LSP隧道,内层为VPN标签(R4分配的),外层为R2到R4的公网隧道,R4到R5也构建双层LSP隧道,内层为VPN标签(R5分配的),外层为R4到R5的公网隧道。在这种情况下,R4和R3之间需要运行某种标签分发协议,目的是分发R4的公网标签,另外,在R4处LSP的内外层标签都会进行SWAP操作,从而把两条LSP粘结成一个端到端的LSP隧道。
配置文件如下:
R1:
R1#sh run
Building configuration...
Current configuration : 906 bytes
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R1
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 1.1.1.1 255.255.255.255
!
interface FastEthernet0/0
ip address 192.168.12.1 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
no ip address
shutdown
duplex auto
speed auto
!
router ospf 1
router-id 1.1.1.1
log-adjacency-changes
network 1.1.1.1 0.0.0.0 area 0
network 192.168.12.1 0.0.0.0 area 0
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
R2:
R2#sh run
Building configuration...
Current configuration : 1682 bytes
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R2
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
ip vrf vpn
rd 100:1
route-target export 100:1
route-target import 100:1
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 2.2.2.2 255.255.255.255
ip router isis
!
interface FastEthernet0/0
ip vrf forwarding vpn
ip address 192.168.12.2 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 192.168.23.2 255.255.255.0
ip router isis
duplex auto
speed auto
mpls ip
!
router ospf 1 vrf vpn
router-id 2.2.2.2
log-adjacency-changes
redistribute bgp 23 subnets
network 192.168.12.2 0.0.0.0 area 0
!
router isis
net 49.0023.0000.0000.0002.00
metric-style wide
!
router bgp 23
no bgp default ipv4-unicast
bgp log-neighbor-changes
neighbor 3.3.3.3 remote-as 23
neighbor 3.3.3.3 update-source Loopback0
!
address-family ipv4
neighbor 3.3.3.3 activate
no auto-summary
no synchronization
exit-address-family
!
address-family vpnv4
neighbor 3.3.3.3 activate
neighbor 3.3.3.3 send-community extended
exit-address-family
!
address-family ipv4 vrf vpn
redistribute ospf 1 vrf vpn match internal external 1 external 2
no synchronization
exit-address-family
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
mpls ldp router-id Loopback0 force
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
R3:
R3#sh run
Building configuration...
Current configuration : 1561 bytes
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R3
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 3.3.3.3 255.255.255.255
ip router isis
!
interface FastEthernet0/0
ip address 192.168.34.3 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 192.168.23.3 255.255.255.0
ip router isis
duplex auto
speed auto
mpls ip
!
router isis
net 49.0023.0000.0000.0003.00
metric-style wide
!
router bgp 23
no bgp default ipv4-unicast
no bgp default route-target filter
bgp log-neighbor-changes
neighbor 2.2.2.2 remote-as 23
neighbor 2.2.2.2 update-source Loopback0
neighbor 192.168.34.4 remote-as 45
!
address-family ipv4
neighbor 2.2.2.2 activate
neighbor 2.2.2.2 next-hop-self
neighbor 192.168.34.4 activate
no auto-summary
no synchronization
exit-address-family
!
address-family vpnv4
neighbor 2.2.2.2 activate
neighbor 2.2.2.2 send-community extended
neighbor 2.2.2.2 next-hop-self
neighbor 192.168.34.4 activate
neighbor 192.168.34.4 send-community extended
exit-address-family
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
mpls ldp router-id Loopback0 force
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
R4:
R4#sh run
Building configuration...
Current configuration : 1561 bytes
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R4
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 4.4.4.4 255.255.255.255
ip router isis
!
interface FastEthernet0/0
ip address 192.168.34.4 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 192.168.45.4 255.255.255.0
ip router isis
duplex auto
speed auto
mpls ip
!
router isis
net 49.0045.0000.0000.0004.00
metric-style wide
!
router bgp 45
no bgp default ipv4-unicast
no bgp default route-target filter
bgp log-neighbor-changes
neighbor 5.5.5.5 remote-as 45
neighbor 5.5.5.5 update-source Loopback0
neighbor 192.168.34.3 remote-as 23
!
address-family ipv4
neighbor 5.5.5.5 activate
neighbor 5.5.5.5 next-hop-self
neighbor 192.168.34.3 activate
no auto-summary
no synchronization
exit-address-family
!
--More--
*Mar 1 01:17:19.415: %SYS-5-CONFIG_I: Configured from console by console
address-family vpnv4
neighbor 5.5.5.5 activate
neighbor 5.5.5.5 send-community extended
neighbor 5.5.5.5 next-hop-self
neighbor 192.168.34.3 activate
neighbor 192.168.34.3 send-community extended
exit-address-family
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
mpls ldp router-id Loopback0 force
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
R5:
Building configuration...
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R5
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
ip vrf vpn
rd 100:2
route-target export 100:1
route-target import 100:1
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 5.5.5.5 255.255.255.255
ip router isis
!
interface FastEthernet0/0
ip vrf forwarding vpn
ip address 192.168.56.5 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
ip address 192.168.45.5 255.255.255.0
ip router isis
duplex auto
speed auto
mpls ip
!
router ospf 1 vrf vpn
router-id 5.5.5.5
log-adjacency-changes
redistribute bgp 45 subnets
network 192.168.56.5 0.0.0.0 area 0
!
router isis
net 49.0045.0000.0000.0005.00
metric-style wide
!
router bgp 45
no bgp default ipv4-unicast
bgp log-neighbor-changes
neighbor 4.4.4.4 remote-as 45
neighbor 4.4.4.4 update-source Loopback0
!
address-family ipv4
neighbor 4.4.4.4 activate
no auto-summary
no synchronization
exit-address-family
!
address-family vpnv4
neighbor 4.4.4.4 activate
neighbor 4.4.4.4 send-community extended
exit-address-family
!
address-family ipv4 vrf vpn
redistribute ospf 1 vrf vpn match internal external 1 external 2
no synchronization
exit-address-family
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
mpls ldp router-id Loopback0 force
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
R6:
R6#sh run
Building configuration...
Current configuration : 906 bytes
!
version 12.4
service timestamps debug datetime msec
service timestamps log datetime msec
no service password-encryption
!
hostname R6
!
boot-start-marker
boot-end-marker
!
!
no aaa new-model
memory-size iomem 5
ip cef
!
!
!
!
no ip domain lookup
!
multilink bundle-name authenticated
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
!
archive
log config
hidekeys
!
!
!
!
!
!
interface Loopback0
ip address 6.6.6.6 255.255.255.255
!
interface FastEthernet0/0
ip address 192.168.56.6 255.255.255.0
duplex auto
speed auto
!
interface FastEthernet0/1
no ip address
shutdown
duplex auto
speed auto
!
router ospf 1
router-id 6.6.6.6
log-adjacency-changes
network 6.6.6.6 0.0.0.0 area 0
network 192.168.56.6 0.0.0.0 area 0
!
!
!
ip http server
no ip http secure-server
!
!
!
!
!
!
!
control-plane
!
!
!
!
!
!
!
!
!
!
line con 0
exec-timeout 0 0
logging synchronous
line aux 0
line vty 0 4
!
!
end
结果验证:
R1#ping 6.6.6.6 sou
R1#show ip route
Codes: C - connected, S - static, R - RIP, M - mobile, B - BGP
D - EIGRP, EX - EIGRP external, O - OSPF, IA - OSPF inter area
N1 - OSPF NSSA external type 1, N2 - OSPF NSSA external type 2
E1 - OSPF external type 1, E2 - OSPF external type 2
i - IS-IS, su - IS-IS summary, L1 - IS-IS level-1, L2 - IS-IS level-2
ia - IS-IS inter area, * - candidate default, U - per-user static route
o - ODR, P - periodic downloaded static route
Gateway of last resort is not set
C 192.168.12.0/24 is directly connected, FastEthernet0/0
1.0.0.0/32 is subnetted, 1 subnets
C 1.1.1.1 is directly connected, Loopback0
6.0.0.0/32 is subnetted, 1 subnets
O IA 6.6.6.6 [110/11] via 192.168.12.2, 00:30:22, FastEthernet0/0
O IA 192.168.56.0/24 [110/11] via 192.168.12.2, 00:30:22, FastEthernet0/0
R1#ping 6.6.6.6 source 1.1.1.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 6.6.6.6, timeout is 2 seconds:
Packet sent with a source address of 1.1.1.1
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max = 172/224/264 ms
R1#traceroute 6.6.6.6
Type escape sequence to abort.
Tracing the route to 6.6.6.6
1 192.168.12.2 84 msec 72 msec 60 msec
2 192.168.23.3 [MPLS: Label 26 Exp 0] 188 msec 248 msec 244 msec
3 192.168.34.4 [MPLS: Label 30 Exp 0] 296 msec 304 msec 212 msec
4 192.168.56.5 [MPLS: Label 19 Exp 0] 184 msec 144 msec 112 msec
5 192.168.56.6 308 msec * 352 msec
R1#
实验总结:这种MPLS VPN的配置相对第一种方法要简单很多,他不需要在AS边界创建VRF,根据不同的情况,BGP边界之间构建单层或双层LSP隧道,当VPN业务发展到一定阶段,BGP边界之间的链路受限时,可以考虑这种跨域方法.
注意事项:在配置的时候需要注意以下几点
1.两边CE的rd不能相同,如果rd相同在PE端不会接受对端路由,会显示为重复忽略.
2.由于跨越了BGP域所以,所以要关闭默认的route-target过滤功能.
3.在AS内部要注意next-hop-self.否则R5收到的next-hop将为192.168.34.3.


发表评论 评论 (3 个评论)